
Structured Cabling & Networking Solutions
End-to-end copper, fiber and wireless infrastructure for reliable voice, data and video connectivity, planned and executed through a disciplined 8-step delivery lifecycle.
Learn MoreNext-Generation Firewalls (NGFW) with Layer 2-7 deep packet inspection, integrated IPS, user identification, content filtering, and granular policy control.

Engineered and integrated according to exact customer requirements, industry standards, and strict service level agreements.
These are deep-packet inspection firewalls that move beyond port/protocol inspection and blocking to add application-level inspection, intrusion prevention, and bringing intelligence from outside the firewall.
These firewalls are third generation advanced security systems and operate on layer 2 to layer 7 of the OSI reference model. It has blended features of a traditional firewall along with advanced features.
These firewalls utilize advanced deep inspection technology, including an integrated intrusion prevention system (IPS), as well as application intelligence and controls.
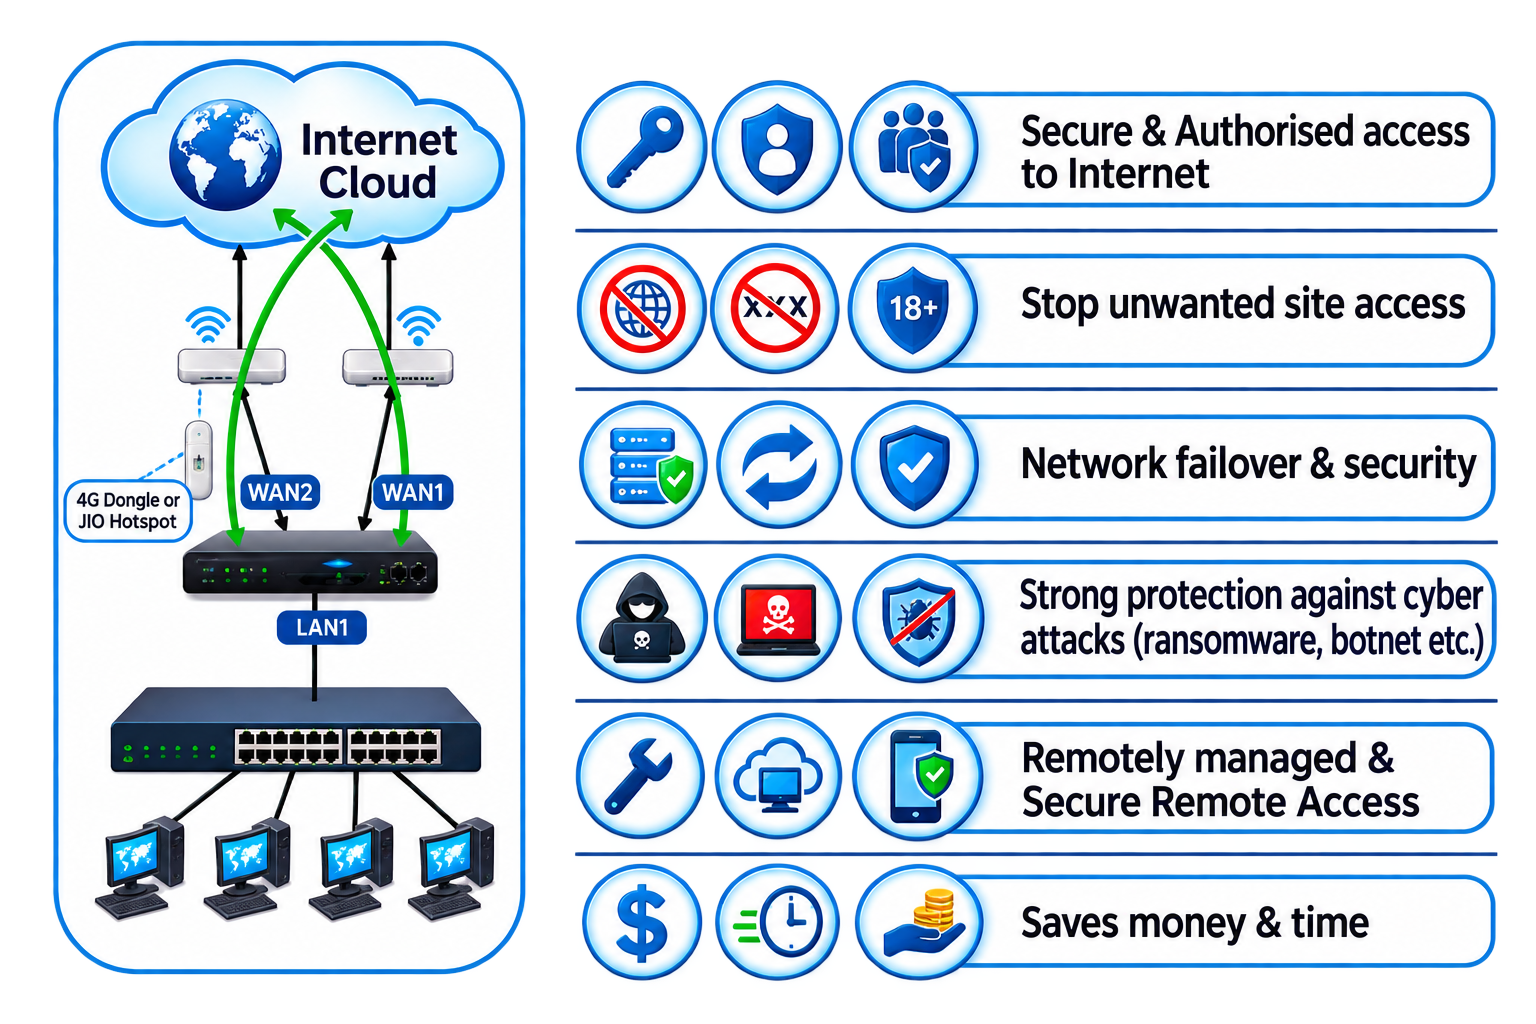
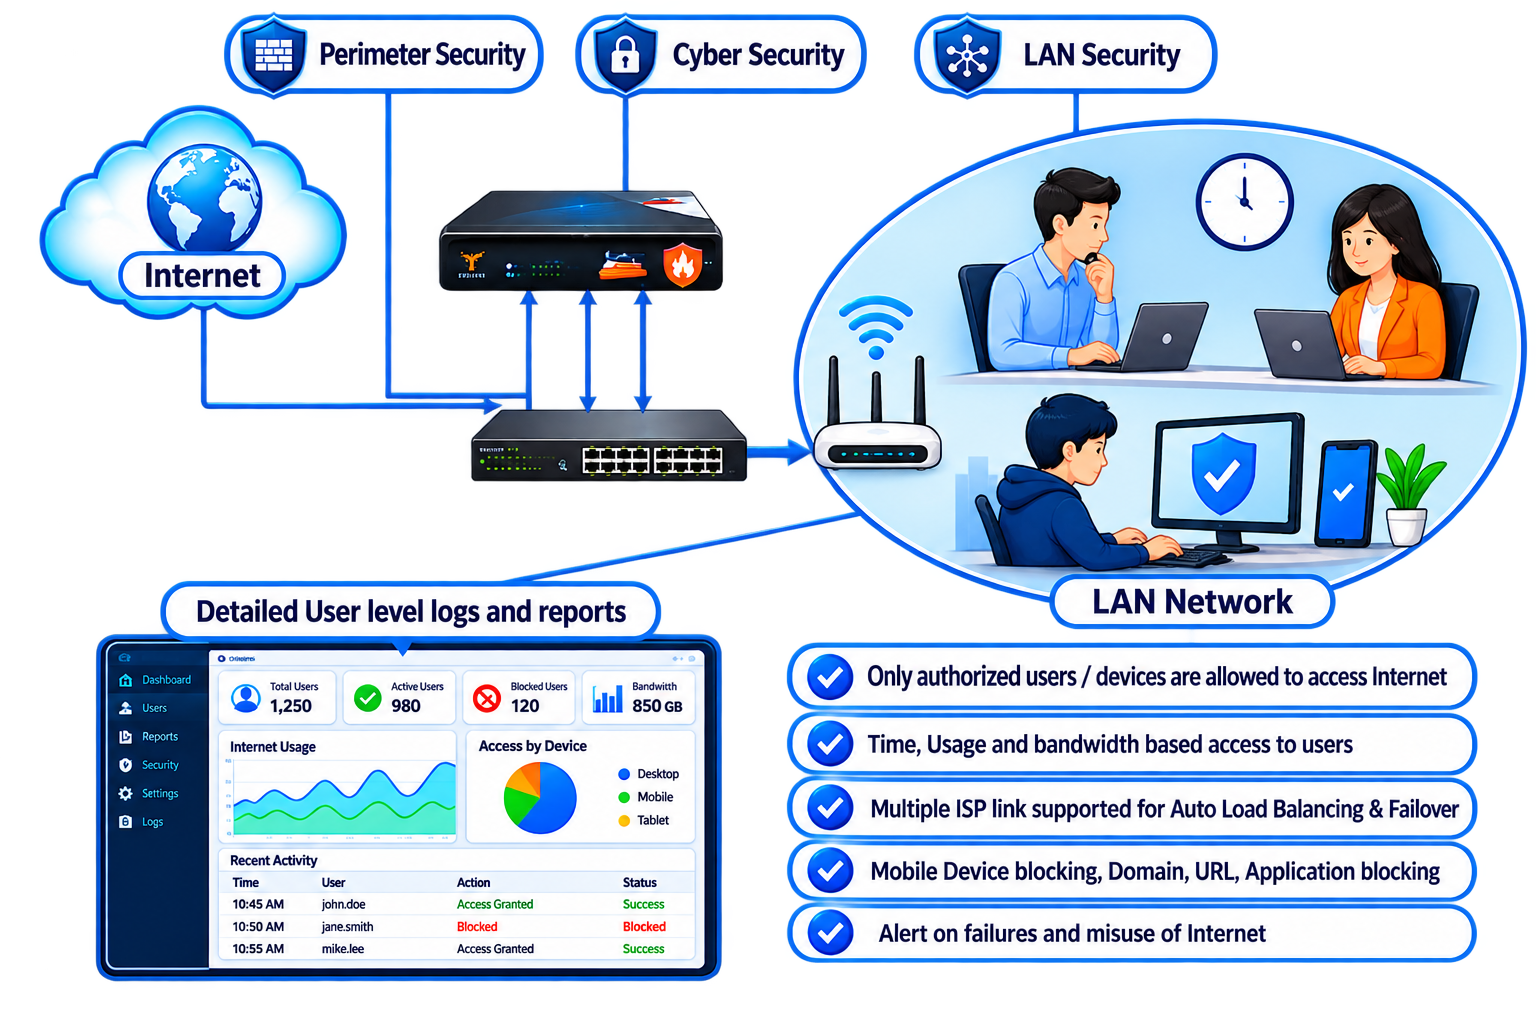
NGFWs can link IP addresses to specific user identities, enabling visibility and control of network activity on a per-user basis. This gains visibility into who specifically is responsible for all application, content, and threat traffic on the network
NGFWs can scan content to prevent data leakage and stop threats with detailed, real-time traffic inspection. This content identification includes Threat prevention, URL filtering and file and data filtering.
An application that might be bad for one organisation might well be good for another. What NGFWs allow is granular levels of control to allow the good aspects of an application to be accessed by the appropriate employees while blocking all access to the bad aspects of an application.
Explore integrated infrastructure services designed to work seamlessly together.
End-to-end copper, fiber and wireless infrastructure for reliable voice, data and video connectivity, planned and executed through a disciplined 8-step delivery lifecycle.
Learn More
Enterprise physical security integrating RFID cards, key fobs, PIN codes, mobile tokens (Bluetooth/NFC), biometrics, electromagnetic locks, and automated gates.
Learn More
Dedicated 1:1 private line connectivity scalable up to 10 Gbps with 99.5% uptime SLA, multiple gateway carrier diversity, centralized firewall, and MPLS routing.
Learn More